What no one sees
It's 3:17 a.m. While most companies are asleep, an alert comes through on one of our clients' systems. Here's what happens in the minutes that follow, and why this invisible work makes all the difference.
A Security Operations Center (SOC) is more than a bank of monitors. It's a chain of human and technical decisions triggered by every suspicious signal, around the clock, every day of the year.
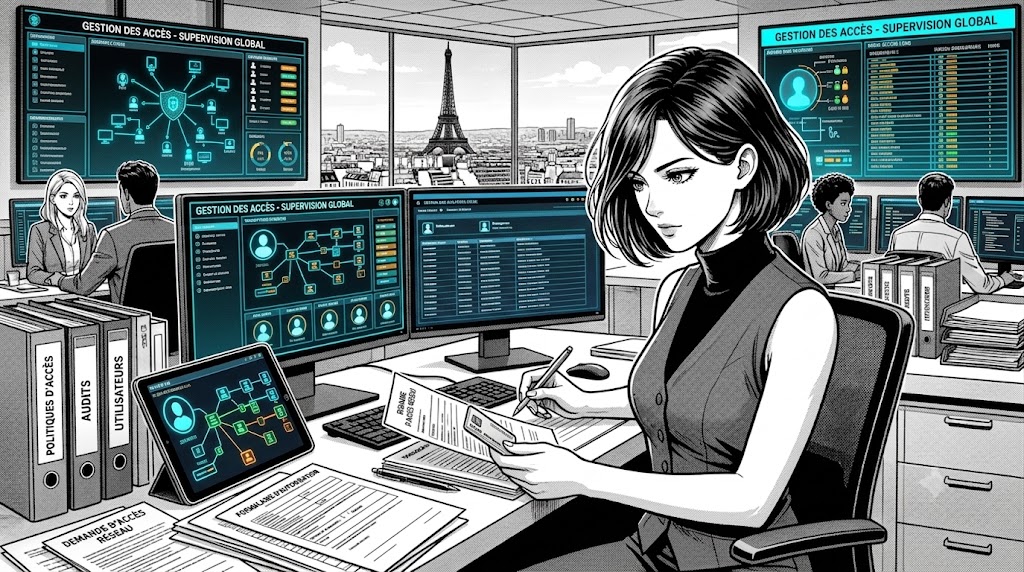
At KYTL, every alert follows a precise path:
1
Detection
Monitoring tools (SIEM, EDR, network probes) flag unusual behavior.
2
Triage
A Level 1 analyst assesses within minutes whether the alert is a false positive or a genuine threat.
3
Investigation
If the threat is confirmed, a Level 2 analyst or threat hunter digs deeper: origin, scope, severity
4
Remediation
Containment measures are triggered, in direct coordination with the client's teams.
5
Reporting
A clear summary is sent to the client, free of unnecessary technical jargon.
A SOC isn't a machine; it's a team. At KYTL, these roles work together:
- The analyst on duty: the first line of defense, triaging and qualifying alerts in real time.
- The threat hunter: doesn't just react: actively searches for weak signals before they turn into incidents.
- The SOC manager: ensures consistency across tools, processes, and client communication.
The people behind the screen
What this means for you
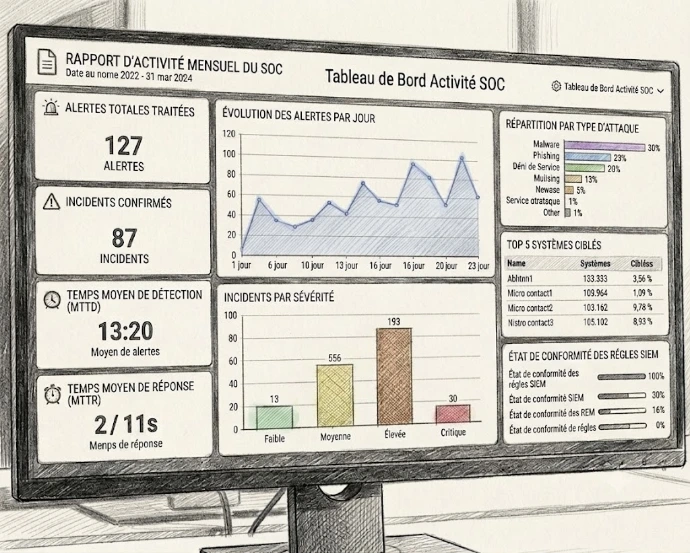
A well-run SOC isn't measured by the number of alerts it handles, but by what it prevents:
- Detection in minutes, not days: the global average time to detect an intrusion still far exceeds 24 hours in companies without continuous monitoring.
- Real coverage outside business hours: nights, weekends, holidays: attacks don't follow office schedules.
- Reporting that speaks your language: not a technical log, but a clear account of what happened and what was done about it.
- A team that knows your environment: not an anonymous, offshored center, but analysts who follow your infrastructure over time.
"Before KYTL, an alert could go unnoticed all weekend. Now we're notified within minutes, with an explanation we actually understand not just another technical ticket."
Head of Security, Industry sector.