The risk no one signed up for
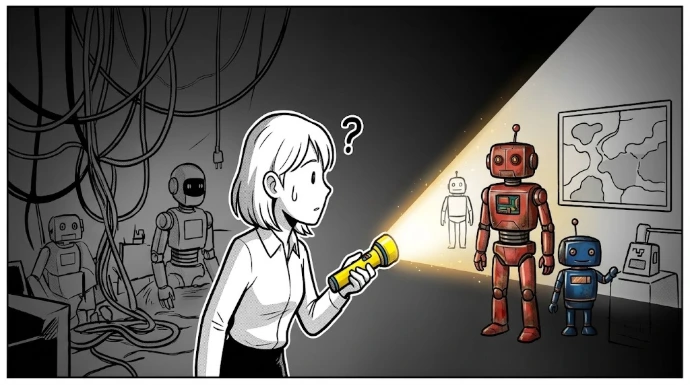
AI adoption inside companies didn't wait for a governance policy. Employees use generative AI tools daily, often without approval, oversight, or any visibility from IT and security teams. This is what's now known as Shadow AI. At KYTL, we help organizations answer four questions most haven't yet asked themselves:
- Discovery: Which AI tools are actually being used across the organization, officially or not?
- Risk assessment: What data is being shared, and what could go wrong if it leaks or gets misused?
- Policy design: What rules make sense for your teams, without blocking productivity outright?
- Ongoing oversight: How do you keep visibility as new tools and use cases keep appearing?
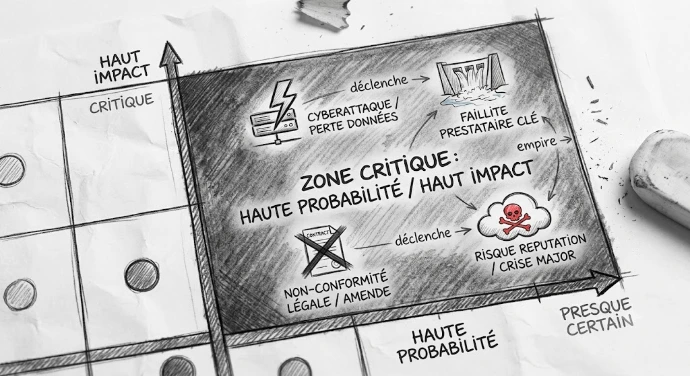
Why this isn't just an IT problem
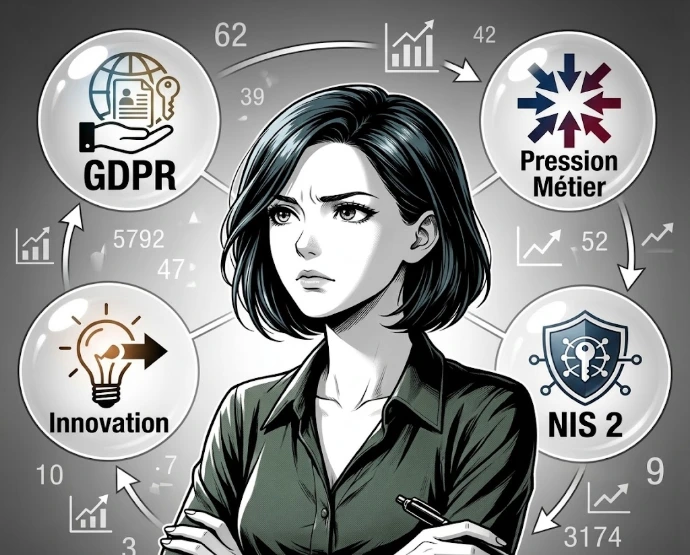
AI governance sits at the crossroads of security, compliance, and business strategy:
- Security teams worry about data leakage and new attack surfaces introduced by AI tools.
- Compliance teams worry about regulations like the EU AI Act and how AI use intersects with existing frameworks (GDPR, NIS2).
- Business leaders worry about losing control of a transformation that's already happening, with or without their approval.
At KYTL, this is treated as one discipline, not three disconnected conversations.
What this means for you
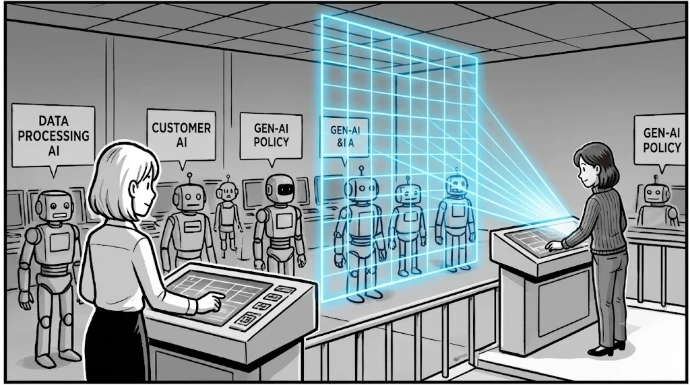
- Visibility where there was none: a clear map of which AI tools are in use, and where the exposure actually is.
- Pragmatic policy, not a blanket ban: rules designed to protect the company without pushing employees toward even less visible workarounds.
- A future-ready posture: as AI regulation matures, your organization won't be starting from zero.
- A bridge between disciplines: one coherent approach instead of security, compliance, and business teams working from different assumptions.
An emerging discipline, built on real depth
AI governance is one of the newest capabilities we've built at KYTL, growing directly out of the same expertise that powers our SOC and risk management work. We're currently working with our clients to put this approach into practice.