Turning uncertainty into a plan
Risk management and governance aren't about producing a report that sits in a drawer. They give leadership a clear, honest picture of exposure and a realistic plan to reduce it.
At KYTL, this work follows a structured path:
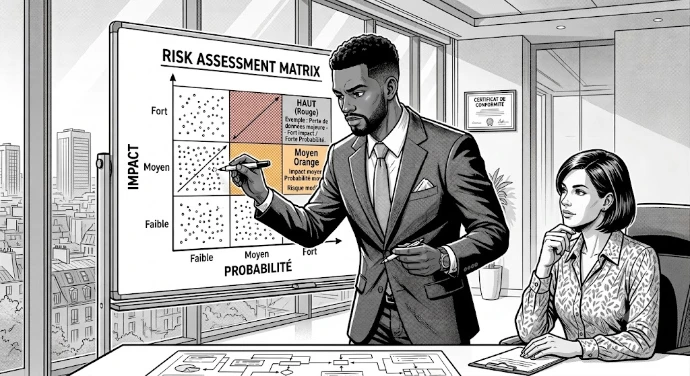
- Risk assessment: Identifying and prioritizing what could actually go wrong, and how much it would cost.
- Regulatory mapping: Understanding exactly which frameworks apply to your organization (NIS2, ISO 27001, DORA, and others).
- Governance design: Defining who owns which decision, and how security fits into the way the company is run.
- Continuous alignment: Keeping the plan current as regulations, threats, and the business itself evolve.
Why this is a leadership issue, not just a technical one
Risk and compliance decisions get made at the top of the organization, whether or not security is in the room:
- Boards are increasingly held accountable: regulations like NIS2 extend personal liability to executives, not just IT teams.
- Compliance without understanding creates false confidence: a checklist completed without real risk analysis behind it protects no one.
- Every business decision carries a risk footprint: new vendors, new markets, new technology all change the picture.
At KYTL, this is why risk and governance work sits alongside, not beneath, our technical services.
What this means for you
- A clear, prioritized view of risk: not a 100-page report no one reads, but a plan leadership can actually act on.
- Confidence in front of regulators and auditors: documented, defensible governance, not last-minute scrambling.
- Decisions made with real visibility: risk considered before it becomes a crisis, not after.
- A governance structure that scales: built to hold as the organization, the threats, and the regulations keep changing.
Expertise built on structure, not guesswork
Risk management and governance are core disciplines at KYTL, connecting our work from SOC operations to identity management.
This expertise relies on:
- Recognized methodologies: our approach is grounded in established frameworks (ISO 27001, NIS2, and other relevant standards), adapted to each organization's real context rather than applied as a generic template.
- A track record across sectors: from major accounts to public sector organizations, we've helped leadership teams turn regulatory obligations into a workable governance structure.
- A team fluent in both languages: our consultants translate technical risk into terms a board can act on, and business priorities into a plan a security team can execute.
This is the discipline that ties the rest of our work together, because a SOC, an identity strategy, or an OT security program is only as strong as the governance decisions behind it.